1 min read

FTC Enforcing That Businesses Patch Log4j Java Security Issue

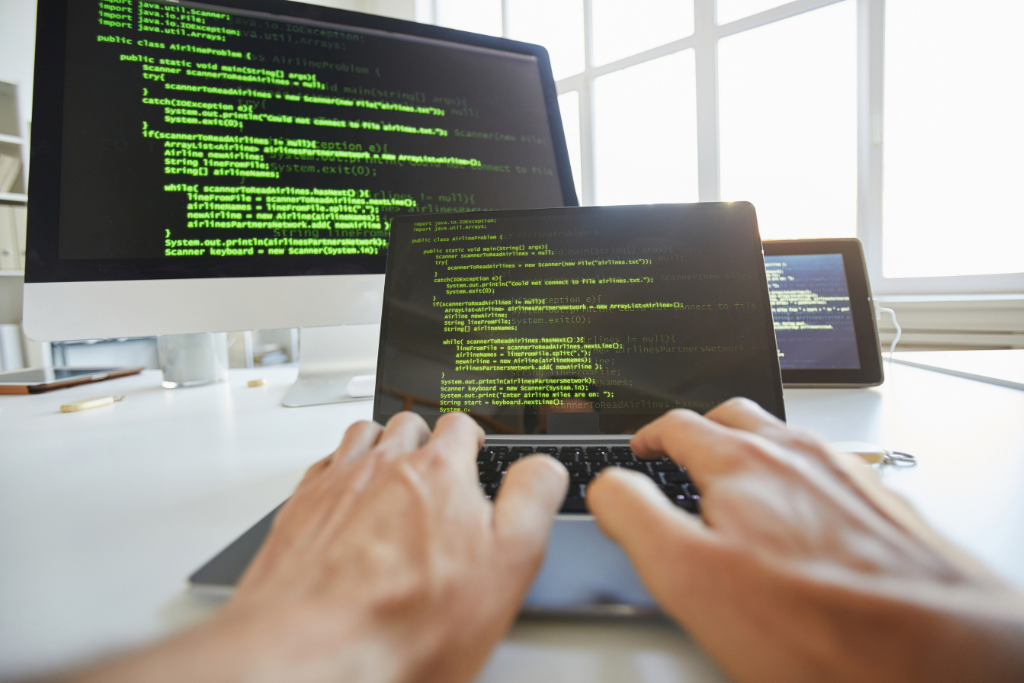
By now you’re almost certainly aware of the Log4j Java issue.

It’s a serious and fixable flaw relating to java logging.

Recently the United States Federal Trade Commission (FTC) has issued a chilling warning to anyone who hasn’t yet fixed the flaw and protected against the vulnerability.

The FTC’s statement reads in part as follows:

“The FTC intends to use its full legal authority to pursue companies that fail to take reasonable steps to protect consumer data from exposure as a result of Log4j, or similar known vulnerabilities in the future. 

Failure to identify and patch instances of this software may violate the FTC Act.

The Log4j vulnerability is part of a broader set of structural issues.  It is one of thousands of unheralded but critically important open-source services that are used across a near-innumerable variety of internet companies. 

These projects are often created and maintained by volunteers, who don’t always have adequate resources and personnel for incident response and proactive maintenance even as their projects are critical to the internet economy.

This overall dynamic is something the FTC will consider as we work to address the root issues that endanger user security.”

The FTC has already made it clear that they’re not playing around with this issue either.  Not long ago in 2019, they hit Equifax with a staggering $700 million fine because of customer data exposure.

The FTC clearly has the muscle to make this threat stick. So if you haven’t already installed the remedy for Long4j, do it now before you lose track of it. Keep an ear to the ground for other similar issues.

These Fines Can Be Devastating

Fines of the sort that the FTC is threatening are enough to rock any business back on its heels. So don’t take any chances.  Stay vigilant out there.  It’s going to be an interesting year.

Used with permission from Article Aggregator

An AI Agent Ran a Ransomware Attack. Alone. The Real Story Is the Aftermath

An AI Agent Ran a Ransomware Attack. Alone. The Real Story Is the Aftermath

The first AI-run ransomware attack wasn't the story. What followed, and what it means for every organization deploying AI agents, is.
Read the full blog
Your IT Provider's Response Time Promise Is Only Worth What They Deliver

Your IT Provider's Response Time Promise Is Only Worth What They Deliver

Your IT provider's response time promise is only worth what they actually deliver. Here's how to read your SLA, what good looks like, and how to...
Read the full blog
Microsoft Copilot vs. ChatGPT for Business: Same Prompt, Very Different Answer

Microsoft Copilot vs. ChatGPT for Business: Same Prompt, Very Different Answer

Most businesses treating Copilot and ChatGPT as substitutes are using at least one wrong. Here's what each is built for and how to choose.

Read the full blog

Why Your Law Firm Needs Managed IT & Data Backups in Portland OR

Data is essential for every law firm. The loss of crucial information can seriously impact operations and harm the firm's reputation.

Read the full blog

WhatsApp Provides Disappearing Messages Feature to Improve Security

WhatsApp has had a tough year from a security standpoint and has suffered losses in the size of its user base as a result.

Read the full blog

Beware Certain Sites Because Of TSA PreCheck Renewal Scam

Fake TSA PreCheck renewal sites are scamming travelers out of $140. These lookalikes are convincing. Always verify the URL before you pay for any...

Read the full blog